Sharing data is now legal and safe. Here's why.
How European data law evolved, what it means for businesses, and how we protect every venue behind our figures.
For years, many companies kept their data to themselves, afraid of breaking privacy rules. European law has since made the path much clearer.
GDPR protects people, not anonymous figures
The GDPR has applied since May 2018. It protects personal data: any information about a person who is identified or can be identified. That made many businesses cautious about sharing any data at all.
But the GDPR itself draws a clear line. Its Recital 26 states that data protection principles do not apply to anonymous information, including data processed for statistical purposes. To decide whether someone could be identified, you look at the means reasonably likely to be used, taking cost, time and available technology into account.
If no one can reasonably be identified, the data is anonymous, and it can be shared.
From protecting data to sharing it safely
Since 2018, Europe has moved from simply protecting data to actively enabling its safe use. These are the key steps.
- May 2018
GDPR applies
Strong protection for personal data. Anonymous data is outside its scope.
- Sep 2023
Data Governance Act applies
Built to increase trust in voluntary data sharing between businesses and citizens, with rules for neutral data intermediaries.
- Jan 2024
Data Act enters into force
The EU's new rules on fair access to and use of data are adopted.
- Sep 2025
Data Act applies, and a key court ruling
On 12 September, most Data Act provisions became applicable, including users' rights to access and share data. A week earlier, the EU Court of Justice (EDPS v SRB) confirmed that data can be personal for the sender but not for a recipient who has no means to identify anyone.
- Nov 2025
Digital Omnibus proposed
The European Commission proposed targeted GDPR changes. They are still being negotiated; the Council has kept the existing definition of personal data.
- Jul 2026
New EDPB guidance on anonymisation
European regulators published draft guidelines that explain, in detail, when data is truly anonymous.
Clearer rules, more trust, better decisions
- Legal certainty. Businesses now have clearer criteria for when shared data is anonymous, and what they must do to keep it that way.
- A right to share. The Data Act gives users of connected products and related services more control over the data they generate, including sharing it with third parties.
- Trust. Regulated, transparent data sharing makes companies more willing to take part, so more data becomes available.
- Better decisions. Brands can base sales and marketing choices on accurate market data instead of estimates and gut feeling.
The rule of 5
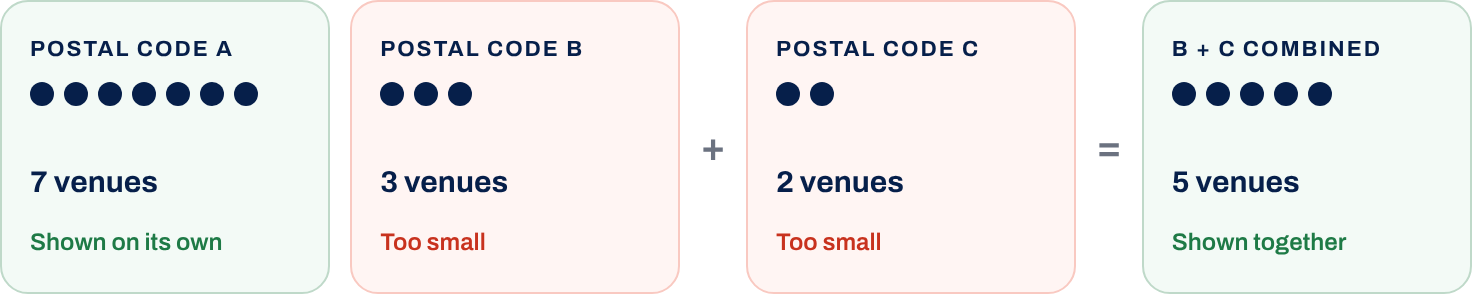
Anonymising data is not just about removing names. The new EDPB guidance stresses that aggregated figures can still reveal information about an individual if the group behind them is too small. If a figure covers only one or two venues, anyone who knows the area could work out who is behind it.
That is why our legal partner set a firm minimum: every figure we show is based on at least 5 venues (points of consumption, or POCs). When a postal code has fewer than 5 venues, we combine it with a neighbouring postal code until the group reaches at least 5.
Facts for brands, protection for venues
Drink brands get accurate, up-to-date facts on prices, venues, promotions and product mix. The bars, cafés and restaurants behind the data, and the people who work and drink there, can't be identified.
All our data is anonymised and used in line with the GDPR and the European Data Act. That is what makes data sharing both legal and safe.
Key takeaways
- Anonymous data is outside the GDPR. When no person can be identified, data protection rules don't apply.
- The EU now actively encourages data sharing, with the Data Governance Act (2023) and the Data Act (2025).
- Courts and regulators have clarified when data counts as anonymous, and for whom.
- At Tea Time Data, every figure is based on at least 5 venues, a rule set by our legal partner, so no single venue can be identified.
This article gives general information. It is not legal advice.
- GDPR, Recital 26: not applicable to anonymous data
- CNPD: The Data Governance Act
- Clifford Chance: EU Data Act, a new era for data sharing has begun
- Osborne Clarke: CJEU clarifies concepts of personal and pseudonymised data
- Cuatrecasas: Digital Omnibus, EU Council establishes position
- E+H: EDPB Guidelines 02/2026 on Anonymisation
Want facts you can trust, from data that's shared safely?
Let's talk data →
Tea Time Data Srl
Av. Arnaud Fraiteur 15/23
1050 Bruxelles, Belgium
contact@teatimedata.com
© 2026 Tea Time Data Srl. All rights reserved.
Terms and conditions · Privacy policy